Overview
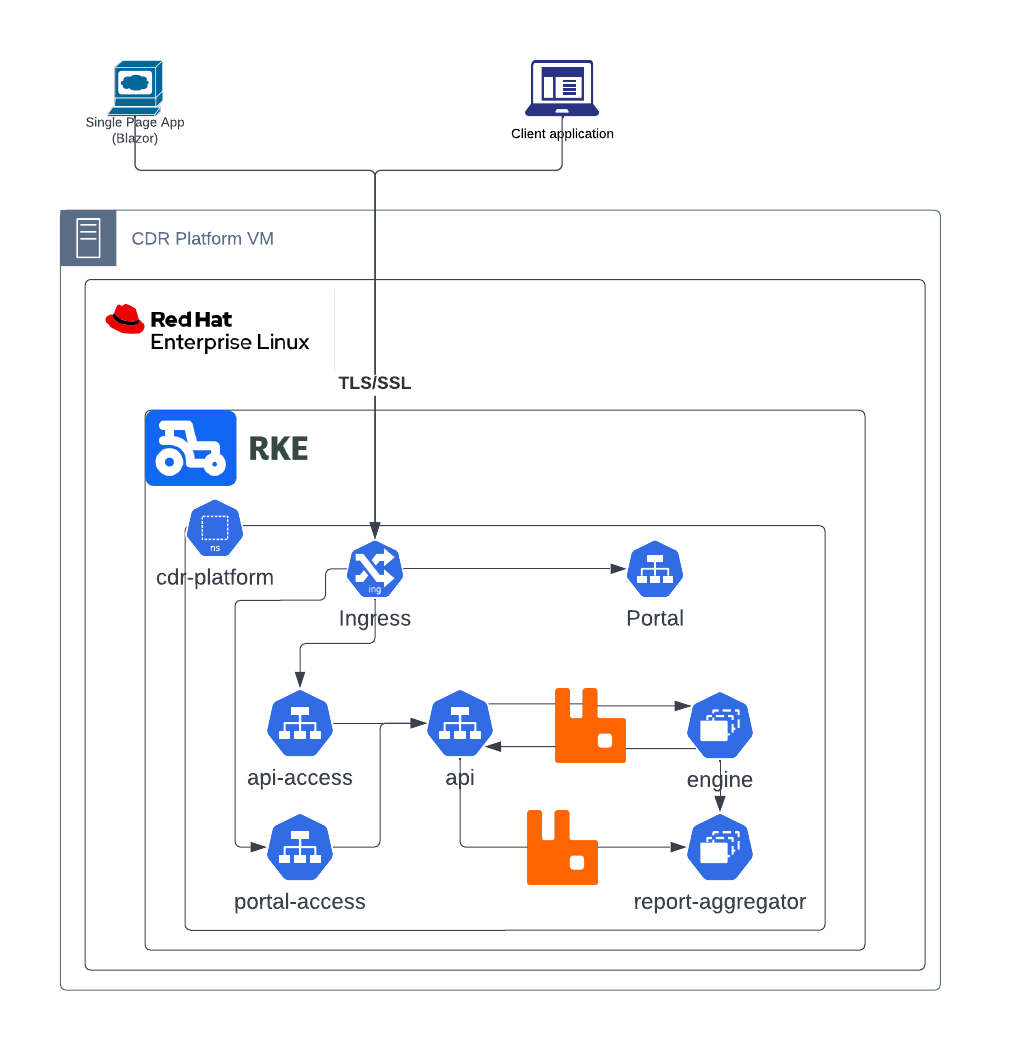
As an alternative to cloud managed kubernetes deployments, the Glasswall Halo can be deployed in a single-node configuration to traditional Virtual Machine infrastructure. This provides an option for deployment to on-premise environments where utilisation of cloud infrastructure is not possible.
Single-node deployments comprises of three main components (for version information, please see the Release Notes):
- Red Hat Enterprise Linux base operating system
- Rancher Kubernetes Engine Government (RKE2) - a Cloud Native Computing Foundation (CNCF) certified Kubernetes distribution
- Glasswall Halo Helm Charts and container images
To simplify deployment of the above components, preconfigured VM images are available in OVA and VHD image formats.
Architecture
Security Posture
The following security hardening procedures have been carried out for each of the main components of the VM deployments:
- Hardened Red Hat Enterprise Linux base operating system
- Hardening utilises the DoD Security Technical Implementation Guides (STIGs) for Red Hat Enterprise Linux
- Rancher Kubernetes Engine Government (RKE2)
- Hardening utilises the Center for Internet Security (CIS) Kubernetes configuration for RKE2
- Glasswall Halo Helm Charts and Container Images
- As per the standard Glasswall Halo deployments, all charts and images are subject to continual SCA, SAST, DAST, IaC and container scanning and associated patching.
Security reports from the above procedures are available on request.
Current Limitations of Single-Node-VM Deployments
When deploying in the single node configuration, scalability is limited to the size of the target VM (or can be manually managed by traditional load balancing). In addition, some functionality may be restricted dependent on the availability of on-prem infrastructure (e.g. databases). For information on functionality, please see the associated Release Notes